• California’s New Employment Laws For 2027: What Employers Need to Know and Do

    By Fred W. Alvarez, Hannah L. Jones, Daniel M. Bruggebrew, Allison Moser, Hannah Withers, Stacey Zartler, and Maya Mercado

    California’s 2026 legislative session has come to a close, and the Governor has signed a number of new employment measures that will affect California employers in 2027 and beyond. The new laws address a range of workplace issues, including AI and automation, pay practices and reporting, leaves of absence, discrimination and harassment, and workplace safety.

    This update highlights the significant employment laws enacted during the recently concluded legislative session, explains their practical implications, and identifies steps employers should consider taking now. Our focus is not simply on what changed, but on what employers need to know and do to prepare for the year ahead.

    AI, Automation & the Workplace

    New Law What Employers Need to Know What Employers Should Do


    SB 947 – Revised No Robo Boss Act


    Beginning July 1, 2027, employers may not rely solely on an Automated Decision System (“ADS”) to make disciplinary or termination decisions in employment. If an ADS is the primary basis for the decision, a human must independently corroborate the decision using the same data relied upon by the ADS. Employers must also notify the employee in writing of the use of the ADS when communicating the decision and provide certain information about the ADS-based decision. Upon request, the employer must provide the employee with a “meaningful, objective description” of the data used by the ADS.

    Employers should identify any ADS used in discipline or termination decisions and establish a human-review process that satisfies the new requirements. Employers should also work with vendors now to understand what data their systems use to make decisions and ensure they are prepared to provide employees with the required information about an ADS-based decision.


    SB 951 – WARN Notice Updates for Layoffs Resulting from AI


    California WARN notices are required when a mass layoff is caused, in whole or substantial part, by AI or other automated technology. The WARN notice must include additional information about the use of the technology, including the job functions being automated. These new requirements take effect on January 1, 2027.


    When planning a potentially covered mass layoff, employers should identify early whether AI or automation is the cause of the employment actions. HR should coordinate with business and technology teams to understand and document the role of the technology and ensure that any required WARN notice includes the necessary information.


    AB 1883 – AI Workplace Surveillance


    Beginning January 1, 2027, employers may not use workplace surveillance tools that use AI to recognize, infer, or predict an employee’s emotional state or that collect neural data.


    Employers should inventory workplace surveillance and monitoring technologies, including tools provided by third-party vendors, and determine whether any features analyze employees’ emotional states or collect neural data.


    Pay Practices & Pay Data Reporting

    New Law What Employers Need to Know What Employers Should Do

    AB 1697 – “Anti-TRAP” Updates


    California’s “anti-TRAP” law, AB 692, took effect on January 1, 2026, restricting employers’ use of training and retention repayment provisions and other “stay-or-pay” arrangements. AB 1697 gives employers additional time—until January 1, 2027—to bring existing agreements into compliance. AB 1697 also makes an important substantive change: it removes the requirement that certain bonus repayment agreements be entered into at the “outset of employment” to be enforceable, potentially expanding the exception to cover retention bonuses and other discretionary bonuses offered later in employment.


    Employers should use the additional compliance period to identify existing agreements and arrangements that require employees to repay bonuses, training costs, or other amounts if they leave employment, and determine whether they comply with the amended law. Employers considering new retention or discretionary bonus programs should also evaluate whether the expanded bonus exception provides additional flexibility in structuring repayment provisions.


    SB 1237 – Increased Penalty for Pay Data Reporting Violations


    For 2027, the penalty for repeated failure to submit required pay data reports increases from $250 to $1,000 per employee. Beginning in 2027, employers must also report employees using the 23 Standard Occupational Classification (SOC) major groups, rather than the EEO-1 job categories previously used for California pay data reporting.


    Employers subject to California’s pay data reporting requirements should update their reporting processes to use the new SOC classifications and begin mapping employees to the appropriate categories well before the filing deadline. Given the significant increase in penalties, employers should also confirm responsibility and timelines for collecting, reviewing, and submitting required pay data.


    Leaves of Absence

    New Law What Employers Need to Know What Employers Should Do
     

    SB 1149 – Expanded Bereavement Leave for a “Designated Person”


    Beginning January 1, 2027, employees may now take up to five days of protected bereavement leave following the death of a “designated person,” which is added to the list of qualifying family relationships. Employers may limit employees to one designated person in a 12-month period.


    Employers should update bereavement-leave policies and leave procedures to include designated persons and train HR personnel and managers on the expanded eligibility requirements. Employers that limit employees to one designated person per 12-month period should also establish a process for tracking those designations.

    Discrimination, Harassment & Workplace Training

    New Law What Employers Need to Know What Employers Should Do
     

    AB 1803 – Anti-hate Speech Training


    Beginning January 1, 2028, employers must incorporate anti-hate speech training and education into California’s required sexual-harassment prevention training. Employers should update their sexual-harassment prevention training materials to incorporate the new anti-hate speech requirements before the January 1, 2028 effective date.


    Workplace Safety

    New Law What Employers Need to Know What Employers Should Do

    AB 1961 – Workplace Violence Restraining Orders


    Beginning January 1, 2027, employers may seek workplace violence restraining orders in broader circumstances. Previously, an employer was required to identify a specific employee who faced a credible threat of violence and name that employee as a protected party. Under the new law, employers may seek an order protecting the workforce more broadly without identifying a specific employee as the target of the threat.  

    Employers should consider pursuing workplace violence restraining orders when threats are directed at the workplace or workforce generally, even if no individual employee has been specifically targeted.


    The Coblentz Employment team is available to answer any questions you may have about the impact of these regulations.
  • Governor Newsom Signs SB 690, Closing One Door on CIPA Claims While Others Remain Open

    By Scott Hall and Phillip Wiese

    The much-discussed California Invasion of Privacy Act (CIPA) amendment, SB 690, has been signed by Governor Gavin Newsom and will take effect January 1, 2027, relieving some pressure businesses face from the flood of litigation, arbitration, and demand letters relating to the use of analytics or marketing technology on their websites.

    Under the new law, private plaintiffs can no longer assert claims under the CIPA pen register and trap and trace provisions, Cal. Penal Code § 638.51. Instead, only the California Attorney General may bring those claims. Additionally, the law is retroactive and applies to any claim filed on or after January 1, 2025. Plaintiffs used this provision to allege that the use of common website analytics tools constituted a pen register or trap and trace device on their computer and, thus, they were entitled to $5,000 statutory damages per violation.

    However, the law will not prevent all CIPA or cookie-based claims going forward. Plaintiffs often paired pen register claims with CIPA wiretapping claims under Cal. Penal Code § 631, which may still be brought by private plaintiffs, and plaintiffs are also pivoting to allege claims under other state and federal laws, including the Electronic Communications Privacy Act, the California Computer Data Access and Fraud Act, consumer protection laws, and others.

    Going forward, companies should remain vigilant about cookie and pixel use on their websites and continue to mitigate risks from those technologies by conducting regular audits and reviews of the specific technology they use. Companies should also confirm that any cookies, pixels, or other third-party analytics tools on their websites are used and operating as described in their privacy disclosures.

    The Coblentz Data Privacy and Cybersecurity team is experienced in handling CIPA claims based on these analytics technologies and advising clients on the best practices for their use to navigate the changing legal landscape. Please reach out to Scott Hall or Phillip Wiese for further information or assistance.

  • Bad Spaniels Bites Back: The Ninth Circuit Narrows Trademark Tarnishment and Restores Parody to the Dilution Analysis

    By Thomas Harvey and Katherine Gianelli

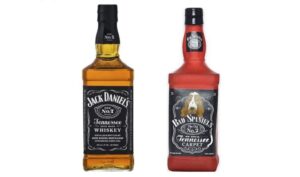
    On August 4, 2026, the U.S. Court of Appeals for the Ninth Circuit issued the latest decision in the long-running trademark dispute between Jack Daniel’s Properties, Inc. and VIP Products LLC over VIP’s “Bad Spaniels” dog toy. The court ruled for VIP, holding that Jack Daniel’s had not proven its parody dog toy damaged the whiskey brand’s reputation.

    The Takeaways

    • Association is not harm. The dilution statute requires proof of association and harm. A parody necessarily satisfies the first—that is the whole point of the joke—but the harm element also needs to be satisfied. The Ninth Circuit confirmed that the plaintiff bears the burden on both.
    • Proof of harm must be about the accused product. Jack Daniel’s expert established only that scatological references repel consumers in the context of food and drink. Nothing in the record connected that to the dog toy. General theory about consumer psychology is not evidence of harm to a particular mark.
    • Fame must be proven mark by mark. A trademark owner cannot borrow the fame of its flagship mark to establish that a label element, tagline, or secondary mark is famous. Each must independently satisfy the statutory factors.
    • Parody still matters on the merits. While the Supreme Court’s ruling foreclosed parody as a threshold escape from dilution liability, it did not make parody irrelevant to whether harm is likely. The Ninth Circuit weighed the toy’s obvious joke in finding that it was not.

    Background

    In 2014, Jack Daniel’s challenged VIP’s squeaky dog toy modeled on the distinctive Jack Daniel’s Old No. 7 Tennessee Whiskey bottle, replacing existing text with scatological jokes. “Jack Daniel’s” became “Bad Spaniels,” “Old No. 7” became “The Old No. 2 On Your Tennessee Carpet,” and the bottle’s alcohol-content language was replaced with phrases including “43% POO BY VOL.” and “100% SMELLY.” toy constitutes both trademark infringement and dilution by tarnishment.

    In 2018, the U.S. District Court found that the Bad Spaniels toy infringed and tarnished Jack Daniel’s trademarks and entered a permanent injunction against VIP. The Ninth Circuit reversed, finding that VIP’s dog toy is an expressive work entitled to First Amendment protection and that the parodic message qualified as noncommercial use. In 2023, a unanimous Supreme Court rejected both holdings (see our prior article on that decision here). Critically, the Court left the merits—specifically the likelihood of confusion and likelihood of tarnishment issues—to the lower courts.

    On remand, the district court found no likelihood of confusion, so VIP won on infringement. But the court held VIP liable for dilution by tarnishment and entered a second permanent injunction. VIP appealed that ruling, and the Ninth Circuit has now reversed it.

    The Ninth Circuit’s Decision

    Fame Must Be Proven for Each Asserted Mark

    While the district court treated Jack Daniel’s marks and trade dress as a collective whole, the Ninth Circuit held that the dilution statute does not permit borrowing the fame of one mark to establish the fame of another. Applying the statutory factors individually, the court found that Jack Daniel’s had proven fame only for the “Jack Daniel’s” word mark and its registered trade dress. Because “Old No. 7” was not separately shown to be famous, the “Old No. 2” joke dropped out of the analysis. “43% Poo by Vol.” likewise had no famous counterpart, because Jack Daniel’s alcohol content language does not function as a trademark. The toy’s most provocative elements thus fell out of the case on a failure of proof.

    Generalized Expert Testimony Was Not Enough

    The Ninth Circuit also rejected Jack Daniel’s expert evidence as insufficient to establish reputational harm. Jack Daniel’s relied on associative-network testimony that linking a beverage to defecation creates consumer disgust. The court found this insufficient: the expert studied no consumer reaction to Bad Spaniels itself, and the record did not establish that a scatological joke on a pet toy affects consumers the way the same joke would on something people drink.

    Parody Still Matters After the Supreme Court’s Decision

    The Supreme Court’s 2023 ruling made clear that parody does not trigger the statutory noncommercial use exclusion when the parodist uses the mark as a source identifier. It did not, however, rule that parody is irrelevant to the dilution analysis—and the Ninth Circuit found it relevant here.

    A successful parody signals both that it evokes the original and that it plainly is not the original. This distinction can reduce the likelihood that consumers will perceive the parody as damaging the reputation of the famous mark. In the Ninth Circuit’s view, the failure of Jack Daniel’s expert to account for Bad Spaniels’ obvious parodic character was a significant flaw in the tarnishment analysis.

    What This Means for Brand Owners

    For brand owners, the decision offers useful guidance for protecting and defending intellectual property.

    • Register the secondary elements, and use them as marks. Alcohol-content language failed because it isn’t a trademark and never functioned as one. Where a label element is doing brand work—a numbered designation, a signature phrase, an estate name—register it and use it consistently as a source identifier rather than as decoration.
    • Understand and address the parodic element. Where a parody is at issue, assess whether the accused use reads as a legible parody, and whether the fame record supports the specific elements copied, before committing to litigation.
    • Decide whether dilution is the right claim before you send the letter. Is the specific element being copied independently famous, and do we have or can we get product-specific evidence of harm? If either answer is no, dilution is the weaker claim, and the case belongs on confusion or on a negotiated resolution.
  • CalPrivacy Targets Gig Economy Platforms In First CCPA Sectoral Audit

    By Scott Hall and Meaghan Henderson

    On July 21, 2026, the California Privacy Protection Agency (CalPrivacy) announced that its newly formed Audits Division has begun its first formal privacy audit, focused on gig economy platforms operating in California. This sectoral audit was initiated in response to hundreds of consumer complaints, as well as comments received during public rulemaking. It reflects CalPrivacy’s continued focus on active enforcement following several high-profile actions earlier in 2026.

    What Is A “Gig Economy Platform”?

    Gig economy platforms are digital applications and websites that connect independent workers with customers for short-term or project-based tasks. Common examples include ridesharing, food delivery, and task-based service platforms.

    Gig economy platforms collect personal information from both customers and the gig workers who provide services through their platforms. The personal information collected by these platforms may be extensive and highly sensitive, and may be used by algorithmic systems to make significant decisions affecting gig workers, including dispatch assignments, performance ratings, compensation, and account suspension or deactivation.

    What Is the Focus of CalPrivacy’s Audit?

    The audit will evaluate whether major gig economy platforms are complying with all obligations under the California Consumer Privacy Act (CCPA) and will focus on whether these platforms provide individuals with meaningful access to and control over their personal information. This emphasis reflects CalPrivacy’s view that access is a foundational right, allowing individuals to identify potential issues and meaningfully exercise other rights such as correction, deletion, and appeal.

    The CCPA’s protections apply to consumers, as well as to employees, job applicants, and independent contractors such as gig workers. Consistent with other California efforts to protect gig workers, the Audits Division also plans to closely examine whether platforms using algorithmic systems as described above are complying with workers’ access rights.

    Failure to comply with workers’ access rights not only violates the CCPA, but may also directly affect workers’ livelihoods. Without access to the information underlying significant decisions, workers may be unable to understand or challenge negative outcomes.

    What Businesses Should Do Now

    Companies that operate a gig economy platform in California or one that targets California residents should review their compliance with the CCPA, including their processes for responding to consumer and worker rights requests.

    Companies should confirm that they have systems in place that allow both consumers and workers to exercise their rights under the CCPA and that access requests are completed within the applicable 45-day statutory period.

    If your company has questions about compliance with the CCPA or whether the audit may apply to your business, the Coblentz Data Privacy & Cybersecurity team can help. Please contact Scott Hall or Meaghan Henderson for additional information or assistance.

  • New California Secretary of State Access Requirements for Third-Party Filings

    The California Secretary of State has changed how third parties may access its online systems to submit filings on behalf of business entities.

    The change is relevant to corporations and limited liability companies formed in California, as well as such entities formed outside California and registered to do business in California, that rely on attorneys, accountants, or other advisors to submit statutory filings.

    Effective July 1, 2026, an entity must grant a third party “Full Access” to its California Secretary of State account before that third party may submit certain filings on the entity’s behalf. Previously anyone was able to submit filings online on behalf of an entity without providing prior authorization. In addition, many documents, such as terminations/dissolutions, could only be processed via physical paper filings, which created processing backlogs and wait times. In an attempt to reduce fraudulent filings and expedite other filings, the Secretary of State has now locked down certain filings for those who have Full Access only. Full Access on the California Secretary of State’s bizfile Online portal[1] allows an authorized user of a business entity to perform certain online transactions, such as Statement of Information filings, conversions and terminations/dissolutions, but only once they have verified their authority with the entity-specific PIN which is mailed to the entity’s last known mailing address.

    Filings that currently require Full Access include:

    Domestic Limited Liability Companies
    •    Statement of Information
    •    Amendment or Attachment to Statement of Information
    •    Certificate of Dissolution
    •    Certificate of Cancellation
    •    Short Form Cancellation Certificate
    •    Conversion/Merger Filings

    Foreign Limited Liability Companies
    •    Statement of Information
    •    Amendment or Attachment to Statement of Information
    •    Certificate of Cancellation
    •    Conversion/Merger Filings

    Domestic Corporations
    •    Statement of Information
    •    Amendment or Attachment to Statement of Information
    •    Certificate of Election to Wind Up and Dissolve
    •    Certificate of Dissolution
    •    Short Form Dissolution Certificate
    •    Nonprofit Certificate of Election to Wind Up and Dissolve
    •    Nonprofit Certificate of Dissolution
    •    Nonprofit Short Form Dissolution Certificate
    •    Conversion/Merger Filings

    Foreign Corporations
    •    Statement of Information
    •    Amendment or Attachment to Statement of Information
    •    Certificate of Surrender
    •    Conversion/Merger Filings

    How to Grant a Third Party Full Access to CA SOS Account

    Obtaining the entity’s unique personal identification number, or PIN, is the first step in granting Full Access. To obtain a PIN for Full Access to an entity’s records, one will need to visit the California Secretary of State’s bizfile Online portal and log in or create an account. The account holder will then search for the entity, select its business record, and select the “Request Access” icon at the bottom of the entity’s profile panel. If the entity has not previously granted anyone access, the state will generate a unique PIN, which will be mailed to the entity’s last known mail address listed on the bizfile Online portal. Once this PIN is received, the account holder will log back into its bizfile account, search for and select the entity, and go back to the “Request Access” icon. The account holder then inputs the PIN to verify authorization and unlock full access to the entity’s records and available online filing functions. With Full Access, one is able to “Manage Full Access” which allows the account holder to assign access control to other users.

    What Businesses Should Do Now 

    Businesses should review who currently has access to their California Secretary of State accounts and determine whether any attorneys, accountants, or other advisors will need Full Access to submit filings on their behalf.

    Entities should address these access requirements well in advance of any filing deadline or transaction closing. Delays in obtaining a PIN or granting access could affect the timely submission of required filings or the entity’s ability to provide evidence of good standing in connection with a transaction.

    We will continue to monitor developments related to these requirements. In the meantime, please contact Peter Wang or Lori Sudowe with any questions.


    [1] https://bizfileonline.sos.ca.gov/

  • New Jersey Enacts the Nation’s Broadest Data Broker Law: What Your Business Should Know

    By Scott Hall and Meaghan Henderson

    New Jersey passed a data broker law (A.5328) that is in effect immediately and is more comprehensive than any similar state law passed to date. The law has two main parts, both with wide reach and significant consequences for noncompliance. Any company that sells personal data of New Jersey consumers should review this law to determine whether its requirements apply.

    Part 1 – Prohibition on the Sale of Sensitive Personal Data

    A.5328 prohibits the sale of New Jersey consumers’ sensitive personal data. “Sale” broadly includes sharing, disclosing, or transferring personal data for monetary or other valuable consideration. “Sensitive data” includes information concerning race or ethnicity, religious beliefs, health, financial accounts, sex life or sexual orientation, citizenship or immigration status, transgender or non-binary status, genetic or biometric identifiers, known children, and precise geolocation.

    This prohibition does not include a consent exception and applies to any company that sells sensitive personal data of New Jersey consumers, even if the company does not meet the applicability thresholds under New Jersey’s general privacy law.

    Selling, offering to sell, or licensing sensitive personal data may result in a civil penalty of $50,000 per record. Because personal data typically moves in high volumes, this could result in substantial penalties for noncompliance.

    Part 2 – Annual Registration and Fees for Data Brokers and Data Collectors

    Unlike other state data broker laws, New Jersey’s law creates a new category of entity—”data collectors”—separate from data brokers. Data collectors are entities that have a direct relationship with consumers but sell or license their personal data to a data broker.

    Both data brokers and data collectors must register annually with the New Jersey Division of Consumer Affairs in the Department of Law and Public Safety and provide information about their data practices. Registration fees range from $5,000 to $1.5 million, depending on the number of consumers involved.

    Failure to register, pay the registration fee, or provide, and maintain, required information may result in a civil penalty of $2,500 per day.

    Below are questions to help you determine whether your company is a “data broker” or “data collector” under New Jersey law.

    Is Your Company a “Data Broker” Under New Jersey Law?

    • Does your company knowingly collect or purchase personal data of New Jersey consumers?
    • Does your company sell or license that data to a third party?
    • Does your company have a direct relationship with the New Jersey consumers whose personal data it collects or purchases?

    If you answered “yes” to the first two questions and “no” to the third, your company is likely a “data broker” and may be subject to the annual registration and fee requirements.

    Is Your Company a “Data Collector” Under New Jersey Law?

    • Does your company knowingly collect personal data of New Jersey consumers?
    • Does your company sell or license that data to a data broker?
    • Does your company have a direct relationship with the New Jersey consumers whose personal data it collects or purchases?

    If you answered “yes” to all three questions, your company is likely a “data collector” and may be subject to the annual registration and fee requirements.

    What Businesses Should Do Now

    Although the public registration requirements do not take effect until March 27, 2027, companies should assess now whether their practices involving the sale, licensing, or sharing of personal data may trigger the law. The potential penalties are significant, and New Jersey regulators are actively reviewing compliance across all sectors.

    If your company has questions about whether this law applies to your business practices, the Coblentz Data Privacy & Cybersecurity team can help. Please contact Scott Hall or Meaghan Henderson for additional information or assistance.

  • California Court Clarifies Standing Under the State’s ALPR Law

    By Scott Hall and Phil Wiese

    The California Court of Appeal recently handed businesses that use automated license plate recognition (ALPR) technology an important victory, holding that a plaintiff must suffer actual harm to have standing to bring a claim under the statute. In Mata v. Digital Recognition Network, Inc., 2026 WL 2085579 (Cal. Ct. App. July 20, 2026), the Court of Appeal affirmed summary judgment, holding that where a business maintains a written ALPR policy, a plaintiff must plead and prove harm distinct from the alleged statutory violation to establish liability.

    Requirements of the California ALPR Statute

    California law requires ALPR operators and end-users to maintain reasonable security procedures and adopt a usage and privacy policy governing the collection, use, maintenance, sharing, and dissemination of ALPR information.[1] The policy must address seven statutory specific topics, including authorized uses, access controls, employee training, security monitoring, data sharing, retention, and destruction. The statute does not otherwise restrict a private entity’s collection or use of ALPR information if it maintains a compliant policy and otherwise complies with security, operational, and other statutory requirements.

    The Recent Mata Court of Appeal Decision

    Plaintiff Guillermo Mata brought a putative class action against Digital Recognition Network, Inc. (DRN), a company that provides license plate recognition services to customers and that housed more than nine billion license plate images in its ALPR system. DRN collected and maintained the images pursuant to an ALPR usage and privacy policy adopted in 2015.

    Plaintiff alleged a single cause of action for violation of the ALPR statute and on behalf of a putative class composed of “[a]ll persons in the State of California whose license plate data was collected by [DRN] using an automatic plate reader.” While DRN’s ALPR policy included the seven items of information required by the statute, the plaintiff claimed that the purpose of the policy was to “maintain the appearance of adhering” to the ALPR statute and “to pay lip service to privacy laws without having any intention of actually complying with them.”

    DRN moved for summary judgment on the basis that the plaintiff suffered no actual harm. DRN conceded that it captured plaintiff’s license plate data at least 15 times. Yet, DRN argued that the plaintiff had not had his identity stolen, nor had he suffered any physical injury, harm, or lost wages as a result of any conduct by DRN. Instead, he testified that the only harm he suffered was that his “privacy ha[d] been violated on multiple occasions.”

    The trial court held, and the Court of Appeal agreed, that actual harm was a necessary component of the statutory standing inquiry. First, under the plain language of the statute, only an individual “who has been harmed by a violation of the statute” has a private right of action to bring a lawsuit.[2] The court concluded that the required harm must be distinct from the statutory violation itself. Because the plaintiff alleged only that the violation invaded his privacy, he failed to establish the requisite harm. The legislature further provided examples of harm under the ALPR statute, including “unauthorized access or use of ALPR information or a breach of security of an ALPR system.”[3] These examples require more than a mere statutory violation.

    Second, the legislative history supported that interpretation. One report referred to damages in actions brought by individuals harmed by the improper use of ALPR data, while another described claims by individuals whose information was unlawfully disclosed. Both examples involved misuse or disclosure of ALPR information—not mere noncompliance with the statute.

    Mata Is In Tension With Another Recent ALPR Decision

    Mata was decided shortly after Bartholomew v. Parking Concepts, Inc., 118 Cal. App. 5th 438 (2026), which we previously discussed here. There, the Court of Appeal determined that the absence of an ALPR policy was a harm that could be the basis for liability under the statute. The court in Bartholomew concluded that collecting and maintaining ALPR information without implementing and publishing the required policy harms individuals and violates their “right to know” who is collecting their ALPR data and for what purposes they are using it.

    The Mata court expressed its skepticism about the “right to know” harm, but distinguished Bartholomew’s limited holding and confined it to businesses without an ALPR policy. In other words, if a business fails to draft and display a written ALPR policy, the absence of that policy may itself satisfy the statute’s harm requirement. By contrast, where a business does adopt and conspicuously post a written ALPR policy, then a plaintiff must show harm distinct from the asserted statutory violation, such as actual harm by the collection or use of the license plate data.

    What Businesses Should Do Now

    Together, Mata and Bartholomew provide businesses with a clearer pathway going forward. Businesses subject to the California ALPR statute applies should promptly confirm that they have an ALPR policy in place. Doing so may reduce risk of lawsuits similar to Bartholomew where a plaintiff can allege a bare statutory violation and will require plaintiffs to suffer actual harm to succeed.

    Additionally, because these ALPR lawsuits are on the rise, businesses that fall within the law’s purview should consider taking the following steps:

    • Identify all locations where cameras or parking systems capture license plate information.
    • Determine whether those systems create or access a searchable database of license plate information.
    • Confirm whether the business is an ALPR “operator,” “end-user,” or both.
    • Review vendor contracts to understand who collects, stores, accesses, shares, and deletes ALPR information.
    • Adopt a written ALPR usage and privacy policy that includes all required statutory elements.
    • Post the policy conspicuously on the business’s website and make it available in writing.
    • Review retention, access, audit, training, and security practices to ensure they match the posted policy.
    • Periodically audit compliance, particularly when deploying new parking, security, or access-control technology.

    If your company needs assistance with any privacy issues, the Coblentz Data Privacy & Cybersecurity team can help. Please reach out to Scott Hall or Phillip Wiese for further information or assistance.

    To view a PDF version of this alert, please click here.


    [1] Cal. Civ. Code § 1798.90.54.

    [2] Cal. Civ. Code § 1798.90.54(a).

    [3] Id.

  • AI Issues Every Human Resources Team Should Be Thinking About Right Now

    By Hannah Withers and Hannah Jones

    Artificial intelligence is rapidly becoming part of everyday Human Resources and People operations—from recruiting and onboarding to performance management and employee relations. But as AI becomes more integrated into these functions, it also creates significant legal and compliance risks. Improper use of AI can expose employers to discrimination claims, compromise confidential and proprietary information, create data privacy concerns, and increase litigation risk. Many organizations are adopting AI tools faster than they are updating the policies, agreements, and governance needed to manage these exposures. Below are several key areas HR and People teams should be evaluating now.

    AI Use Policies for HR

    Many HR teams are already using AI tools, often without clear internal guidance on what is and is not permitted. Without a written policy, organizations face discrimination, equity, data security, and other employment compliance risks.

    Key topics for an AI Use Policy include:

    • Which AI platforms are approved for HR use and under what circumstances?
    • May AI be used to assist with hiring, promotion, discipline, or termination decisions, and if so, what level of human review is required?
    • What types of employee data may or may not be entered into AI tools?
    • How should AI-generated outputs be documented and retained?

    Privilege and Litigation Risks

    One of the most significant, and often overlooked, risks of AI use in HR is that conversations with AI tools may not be protected by attorney-client privilege. When HR personnel use AI to answer legal questions or evaluate employee complaints, those prompts and responses may be discoverable in litigation. If an AI tool flagged a potential legal violation and the company proceeded with a contrary course of action, that record could become powerful evidence for the opposing party. Organizations should think carefully about where legal questions are being routed and whether AI-generated records are being preserved in accordance with litigation hold obligations.

    Employment Agreements and Internal Policies

    Many employers’ confidentiality agreements, proprietary information and inventions assignment agreements (PIIAAs), independent contractor agreements, and employee handbooks were drafted before the widespread adoption of generative AI. These documents may not address whether employees can use AI tools to perform their work, who owns AI-generated work product, or what happens when confidential information is entered into a third-party AI platform. Employers operating with pre-AI-era agreements may have gaps in their protections that are worth examining.

    AI in Hiring and Employment Decisions

    The use of AI in hiring and employment decisions is one of the most heavily regulated and scrutinized areas of AI in the workplace. Organizations using AI at any stage of the hiring process (e.g. resume screening, candidate ranking, skills assessments, or interview evaluation) face potential exposure under federal anti-discrimination law and a growing patchwork of state and local AI regulations.

    Key concerns include the risk that AI tools may perpetuate historical patterns of discrimination, resulting in disparate impact claims. Several jurisdictions (including California, Connecticut, New York City, Illinois, Maryland, and Colorado) have enacted or proposed laws requiring disclosure, bias audits, or other compliance steps when AI is used in employment decisions. These requirements are expanding rapidly, and employers using AI-powered tools to make important employment decisions should be aware of their obligations in each jurisdiction where they operate.

    Beyond hiring, similar concerns arise when AI tools are used in performance management or termination decisions. If an algorithm recommends adverse action and a discrimination claim follows, the employer may need to explain and defend the AI tool’s methodology, raising questions about transparency, documentation, and the role of human oversight.

    Recent litigation over alleged AI-assisted layoff selection underscores that these risks are not limited to hiring and remain largely uncharted territory. Employers using AI or algorithmic inputs in reductions in force, performance rankings, or other selection decisions should expect increased scrutiny of disparate impact, disability and leave-related bias, and the adequacy of human oversight.

    Data Privacy and Cross-Border Considerations

    AI use by HR frequently involves processing data reflecting employee and applicant personal information. Employers subject to the California Privacy Rights Act (CPRA), other state privacy laws, or international data protection frameworks should review their employee and applicant privacy notices to ensure they accurately describe how personal information is collected, used, disclosed, retained, and, where applicable, processed using AI tools. Employers should also confirm that their use of AI complies with applicable privacy requirements, including obligations relating to data minimization, purpose limitation, and vendor management.

    Emerging Issues to Watch

    As organizations incorporate AI into broader HR functions, several additional areas are drawing legal and regulatory attention:

    • Pay Equity: AI tools used to set compensation or determine pay bands may inadvertently perpetuate pay disparities, raising concerns under federal and state equal pay laws.
    • Workplace Monitoring: AI-powered productivity tracking and surveillance tools face increasing regulatory scrutiny, with several states considering or enacting legislation requiring notice and consent.
    • Accommodations and Leave: AI tools used to evaluate disability accommodation requests or manage leave entitlements must account for the individualized assessment requirements of the ADA, FMLA, and analogous state laws.
    • Religious Accommodations: Employees may raise religious objections to mandatory AI tools, potentially triggering accommodation obligations that employers will need to navigate.
    • Vendor Contracts: Organizations purchasing AI tools from third-party vendors should consider whether their contractual arrangements appropriately account for the legal, operational, and business risks associated with the use of those tools.

    The Bottom Line

    The legal landscape around AI in the workplace is evolving quickly, and the compliance obligations are only becoming more complex. Organizations that have not yet assessed how AI intersects with their HR practices may find themselves exposed to risks they haven’t fully considered. The issues above are not exhaustive, but they represent the areas where we are seeing the most activity and where early attention can make a meaningful difference.

    If you have questions about how these developments may affect your workplace policies, please contact any member of the Coblentz Employment Group.

    To view a PDF version of this article, please click here.

    This alert is intended to provide general information and does not constitute legal advice. Each situation is fact-specific, and you should consult with counsel regarding your particular circumstances.

  • California ALPR Litigation Is on the Rise: Parking Operators, Retailers, and Property Owners Should Review (Or Prepare) Their ALPR Policies

    By Scott Hall and Phillip Wiese

    Businesses that use automated license plate recognition (ALPR) technology should take a fresh look at their compliance with California’s Automated License Plate Recognition law. A recent California Court of Appeal decision, followed by several new class action complaints, has increased litigation risk for parking operators, shopping centers, retailers, property managers, and other businesses that use ALPR technology but have not adopted and publicly posted a compliant ALPR usage and privacy policy.

    California’s ALPR statute, Civil Code sections 1798.90.5–1798.90.55, has been in effect since 2016, but many private businesses are not aware of the law’s requirement to post an ALPR policy or may not realize that the statute applies beyond law enforcement or dedicated parking technology companies. The law can apply to private entities that operate, access, or use systems that capture license plate information through cameras and convert that information into searchable computer-readable data.

    The Policy Requirement

    California law requires ALPR operators and end-users to maintain reasonable security procedures and implement a usage and privacy policy governing the collection, use, maintenance, sharing, and dissemination of ALPR information. The required policy must address specific topics, including authorized purposes for using ALPR information, who may access it, training requirements, security monitoring, sharing restrictions, data accuracy measures, retention periods, and destruction procedures. In Bartholomew v. Parking Concepts, Inc., the Court of Appeal summarized these requirements and emphasized the requirement to publicly post the policy in writing, and, if the business has a website, conspicuously post the policy on that website. 

    Why the Risk Has Increased

    The key recent development is the February 2026 Bartholomew decision. In that case, a plaintiff alleged that a parking garage operator collected his license plate information when he entered and exited a garage but failed to implement and make publicly available the required ALPR usage and privacy policy. The trial court sustained the parking garage operator’s demurrer, but the Court of Appeal reversed in part.

    The most important part of the decision is the Court of Appeal’s ruling on “harm.” The ALPR statute authorizes a private civil action only by an individual “harmed” by a violation. The parking garage operator argued that a plaintiff must show misuse, mishandling, or measurable damages—not simply lack of compliance with statutory requirements. The Court of Appeal disagreed. Although the court held that a mere technical violation is not always enough, it concluded that collecting and maintaining ALPR information without implementing and making public the required policy harms individuals by violating their statutory “right to know” who is collecting their ALPR data and how it is being used and maintained.

    That holding is significant because the statute provides for actual damages, but not less than $2,500 in liquidated damages, along with potential punitive damages, attorneys’ fees, litigation costs, and injunctive relief. 

    New ALPR Lawsuits Are On The Rise After Bartholomew

    Since Bartholomew, plaintiffs’ firms have filed new putative class actions against businesses and property owners that allegedly used ALPR technology without the required public policy. Complaints have even been filed against businesses that have posted ALPR policies, but which plaintiffs assert lack information or details required by the statute.

    What Businesses Should Do Now

    Businesses that use ALPR technology in parking lots, garages, retail centers, residential communities, office properties, hospitals, or other facilities should promptly determine whether the California ALPR law applies to them. This review should consider facilities the business operates directly, as well as those operated by vendors, parking managers, security contractors, or property management companies.

    At a minimum, businesses should consider taking the following steps:

    • Identify all locations where cameras or parking systems capture license plate information.
    • Determine whether those systems create or access a searchable database of license plate information.
    • Confirm whether the business is an ALPR “operator,” “end-user,” or both.
    • Review vendor contracts to understand who collects, stores, accesses, shares, and deletes ALPR information.
    • Adopt a written ALPR usage and privacy policy that includes all required statutory elements.
    • Post the policy conspicuously on the business’s website and make it available in writing.
    • Review retention, access, audit, training, and security practices to ensure they match the posted policy.
    • Periodically audit compliance, particularly when deploying new parking, security, or access-control technology.

    Conclusion

    The recent wave of ALPR litigation shows that businesses may face legal claims not only arising from the collection or use of license plate data, but also from the absence of a posted, statute-compliant policy. After Bartholomew, one of the most important steps businesses can take to reduce litigation exposure is to adopt and post a compliant ALPR policy.

    If your company needs assistance with any privacy issues, the Coblentz Data Privacy & Cybersecurity team can help. Please reach out to Scott Hall or Phillip Wiese for further information or assistance.

  • When Capacity Becomes A Catch-22: Defining Your Clients’ Due Process Rights After Herren

    Jennifer Scharre and Frank Busch authored “When Capacity Becomes A Catch-22: Defining Your Clients’ Due Process Rights After Herren” which was published in the California Trusts & Estates Quarterly. Their article examines the far-reaching implications of Herren v. George S. and offers guidance and sample trust provisions to help settlors protect themselves. The full article is linked here.